End-to-End DevSecOps Pipeline for Netflix Clone.
A secure, automated deployment pipeline that packages, scans, and deploys a containerized application to EKS using GitOps.
The objective
Create a repeatable deployment workflow for a Netflix clone that brings security scanning and GitOps delivery into the same pipeline.
Architecture & implementation
Built a Jenkins-driven pipeline with SonarQube and Trivy scanning, Docker image builds, Helm packaging, and ArgoCD GitOps delivery to EKS.
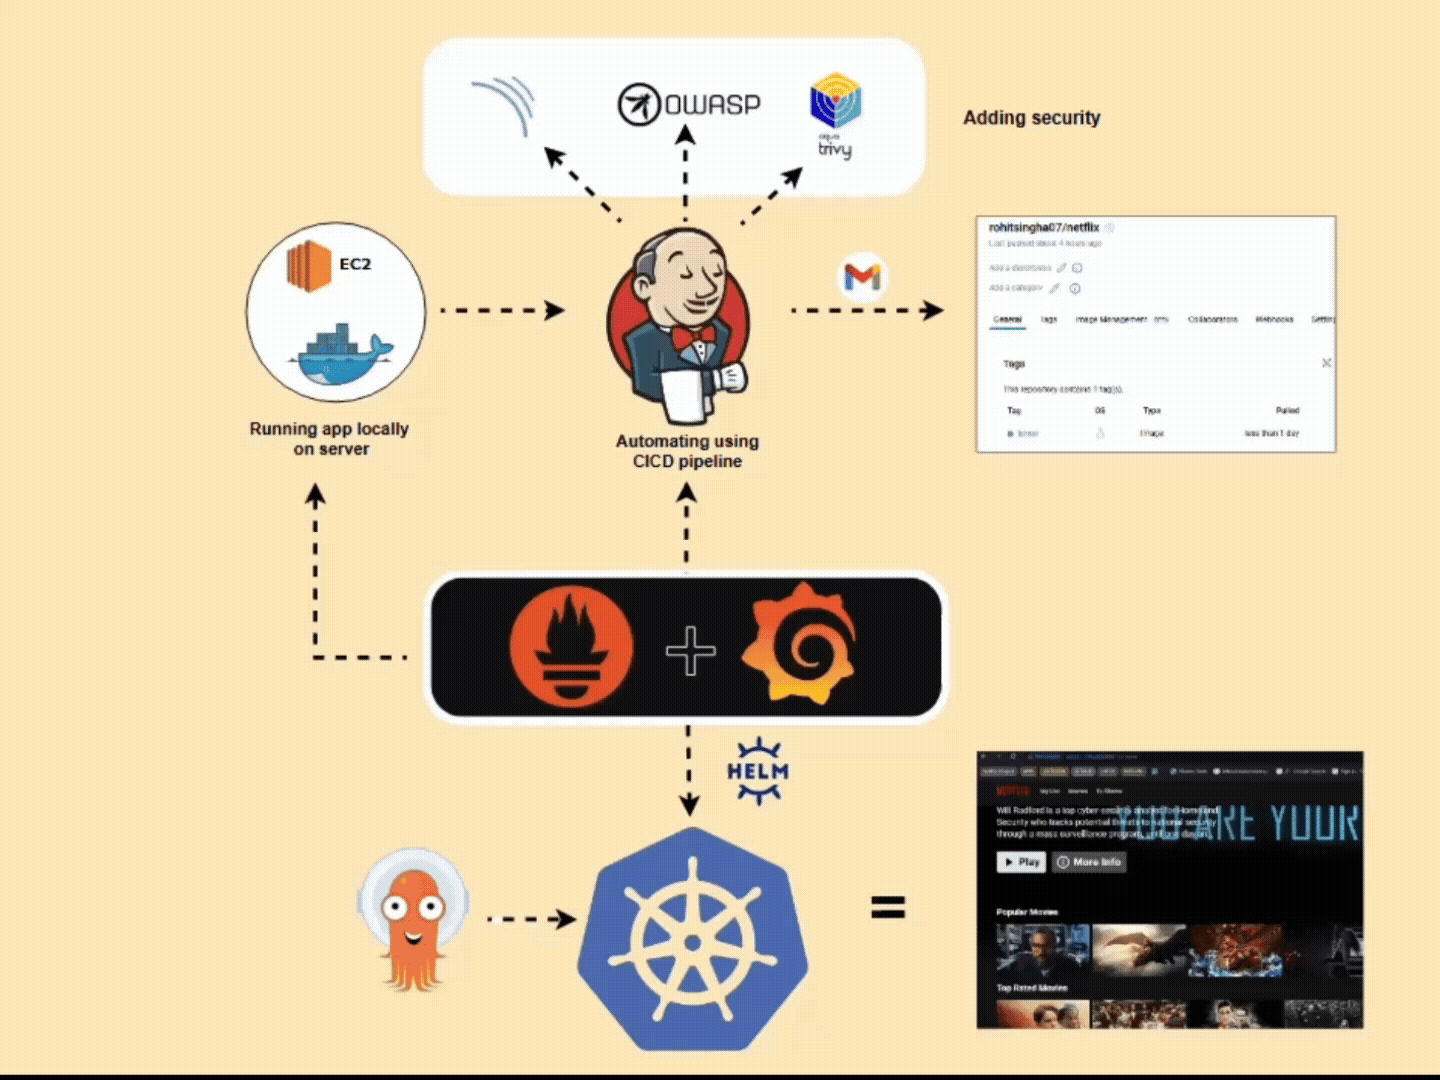
- GitHub
- Jenkins
- SonarQube / Trivy
- Docker
- Amazon ECR
- Helm
- EKS
- Prometheus / Grafana
Key components of the implementation.
My contributions & decisions
Security in the delivery path
Integrated SonarQube and Trivy scanning into the Jenkins pipeline to check application code and container images.
GitOps delivery
Automated deployment to Amazon EKS with Jenkins and ArgoCD, using Docker and Helm in the delivery toolchain.
Operational visibility
Included Prometheus and Grafana in the project’s observability toolchain.
The outcome
Increased deploy frequency by 40% and vulnerability detection coverage by 50%.